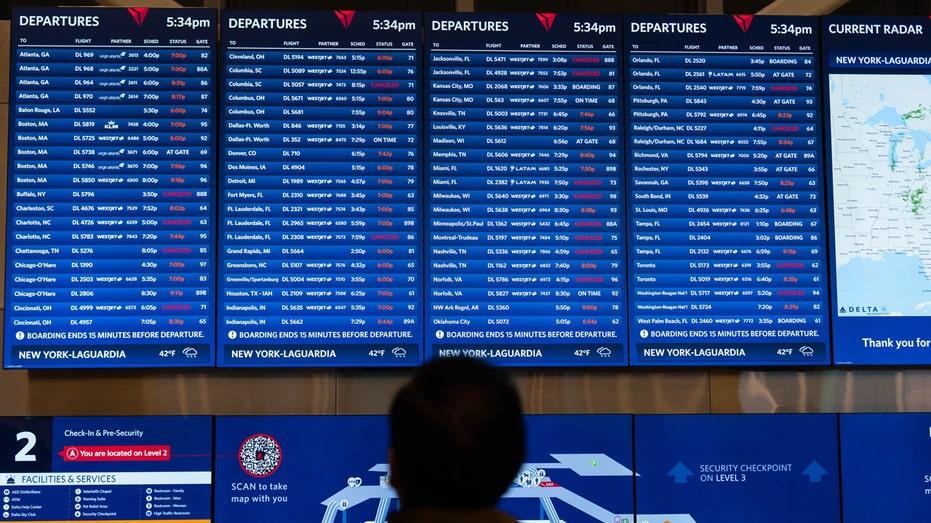
In the wake of a disruptive week that saw a nationwide FAA ground stop, major banking outages at JPMorgan Chase, and a Microsoft service disruption, officials were swift to declare that no malicious activity was behind the failures, with Homeland Security Secretary Markwayne Mullin and Director of National Intelligence Jay Clayton stating there was no evidence of a coordinated or state-sponsored attack, attributing the incidents to routine maintenance and technical changes. However, Danny Cooper, CEO of critical infrastructure security firm SMET, argues that such definitive pronouncements are premature and improbable, questioning the likelihood of multiple critical systems experiencing independent technical failures within such a short timeframe and suggesting that ruling out foul play too quickly bypasses essential, time-consuming forensic investigations. Cooper posits that the rapid dismissal of cyberattack possibilities, especially before thorough audits, can deepen public suspicion and that sophisticated adversaries actively monitor these maintenance windows, potentially exploiting them to inject malware and exploits, making the assertion of ‘no malicious activity’ without complete investigation a potentially flawed and risky conclusion.
Adapted from: U.S. News Today on Fox News